
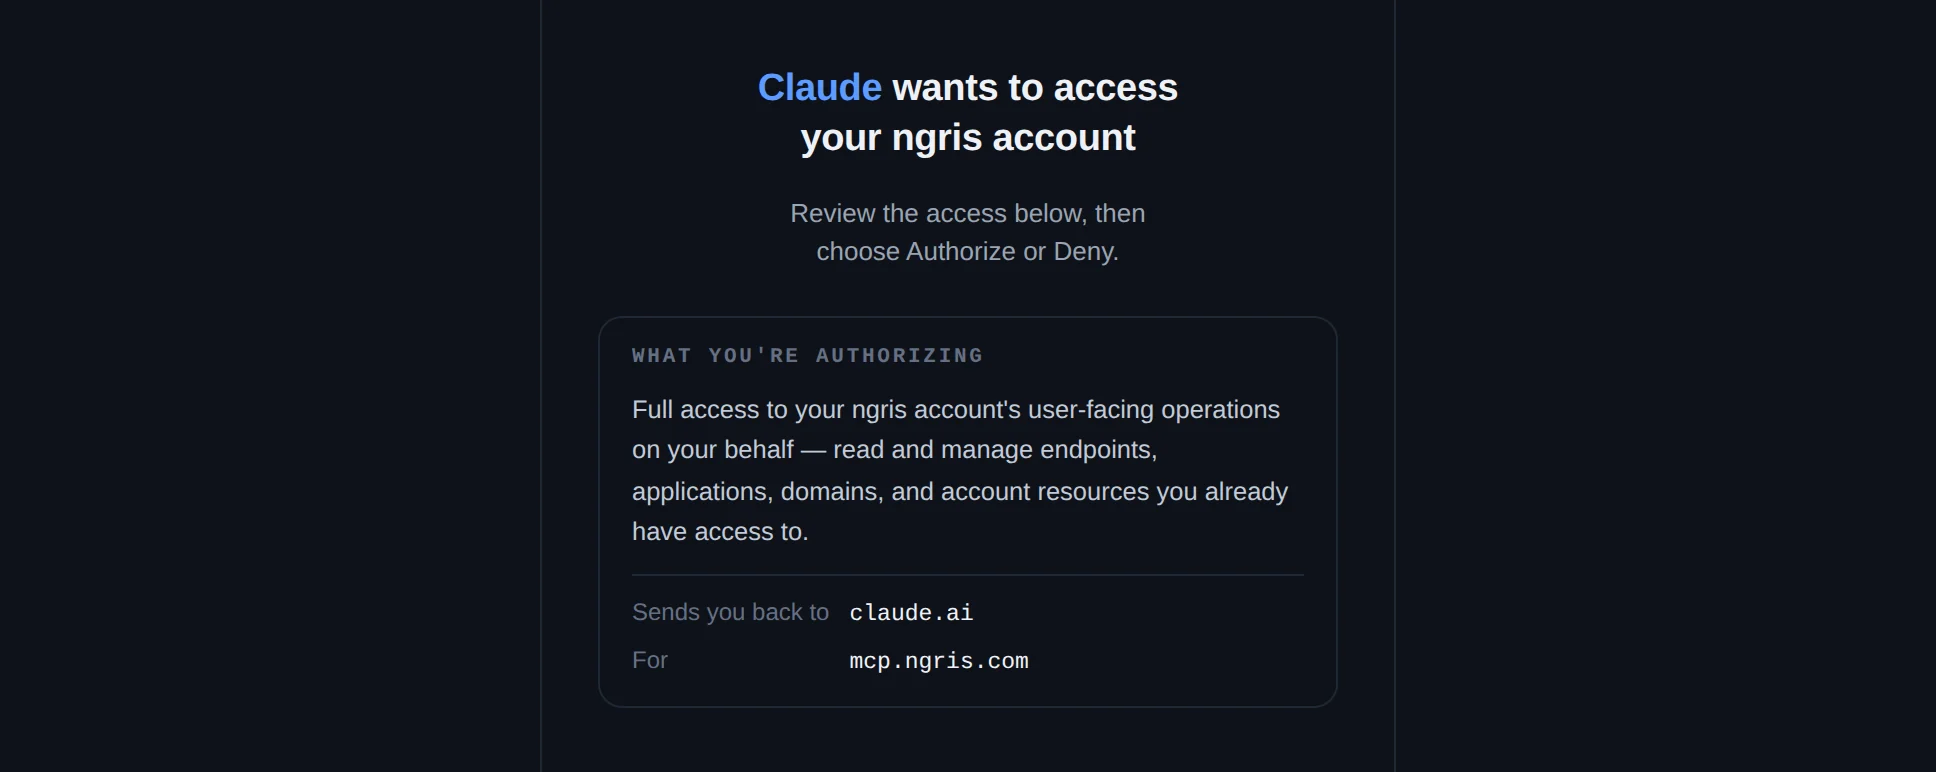
When an assistant connects to ngris over MCP, you approve it on an ngris page. That page named the app, and an app can call itself anything.
Now the page also shows where the app sends you back after you approve, and which ngris service the token is for. Above, Claude asks to connect: it sends you back to claude.ai, for mcp.ngris.com.
What changed
- Where you go back. The approval page shows the website the app returns you to, or an app on this computer for a desktop client. Approve only when it is the app you are connecting.
- Tokens work only with ngris. An app can ask for a token only for an ngris service. A request for any other site is refused before you are asked.
- An MCP session stays an MCP session. Switching or creating accounts, changing your password and signing out other sessions return no dashboard sign-in to an MCP app. The same holds for API keys.
- Signing out reaches MCP apps. Signing out other sessions from an MCP app, or with an API key, signs out every session, that MCP app included. Connect it again afterwards.
- Private keys need write access. Downloading a certificate with its private key needs the Certificates write permission, the one that uploads certificates. Read still lists them.
- Site backups need write access. Downloading the files of an app backup (for WordPress, with
wp-config.php) needs Endpoints write. A database dump still needs Database data read. - For client developers. The authorization response names the issuer (
iss), aresourceoutside ngris answersinvalid_target, an authorization code presented twice revokes the refresh tokens issued from it, and the registration and token endpoints answer apps that run in a browser.
Get started
- Connect your MCP client as before. On the approval page, check Sends you back to before you click Authorize.
- If someone in your account downloads certificate keys or app backups with a custom role, give that role Certificates write or Endpoints write under Account → Roles.
- Read the docs: MCP authentication, Roles and permissions and Download a certificate.